Anthropic’s September 2026 misuse report: the loops that matter and the four gates that hold
Anthropic has published a 154-page report on threat actors misusing Claude: hackers, governments, scammers, commercial spyware operations, and weapons developers. The headlines are loud. The useful part is quieter: AI is not only answering questions anymore. It is running loops.
We read the report so we could separate what it documents from what is being repeated badly. Two things worth fixing up front: the Ukraine/drone espionage case in the report is GTG-20006, and the report says its primary access technique was not a zero-day at all — it was device code phishing against Microsoft 365.
Everything below that comes from the report is attributed to it. Everything else — the thesis, the ordering, the recommendations — is our reading.
The case to read first: GTG-20006
Anthropic links GTG-20006 to tradecraft consistent with Midnight Blizzard. According to the report, the actor targeted more than 20 organizations: government ministries, defense and intelligence bodies, embassies, think tanks, and defense-industrial companies, mostly in Ukraine and Europe.
How they got in
The technique behind that access was device code phishing against Microsoft 365, run through an “Embassy Kit” framework that the report says yielded mail records from at least eight organizations.
Around that phishing, Anthropic describes the usual modern intrusion surface: ClickFix-style lures, DNS hijacking, and compromised hotel guest WiFi used to stage malware for Windows, Android, and iOS.
If you run Microsoft 365, our reading is that the single highest-value mitigation in this report is also the most unglamorous: block the device code flow in Conditional Access, then audit the device-code grants that already exist. Refresh tokens survive password resets, so a password-rotation campaign will not close this one.
What they took
The theft that matters for technology companies, as the report describes it: the actor bulk-exported mailboxes from at least two drone component manufacturers, targeted a military drone maker, and stole a complete proprietary software development kit for a drone vision system.
Anthropic says it then spent several days reverse-engineering that system, recovering product architecture, hardware bill of materials, supplier dependencies, and details of an unannounced product.
That is the uncomfortable part, and it is ours rather than the report’s: a stolen SDK is no longer just stolen IP. It is a prompt.
The malware now rebuilds itself
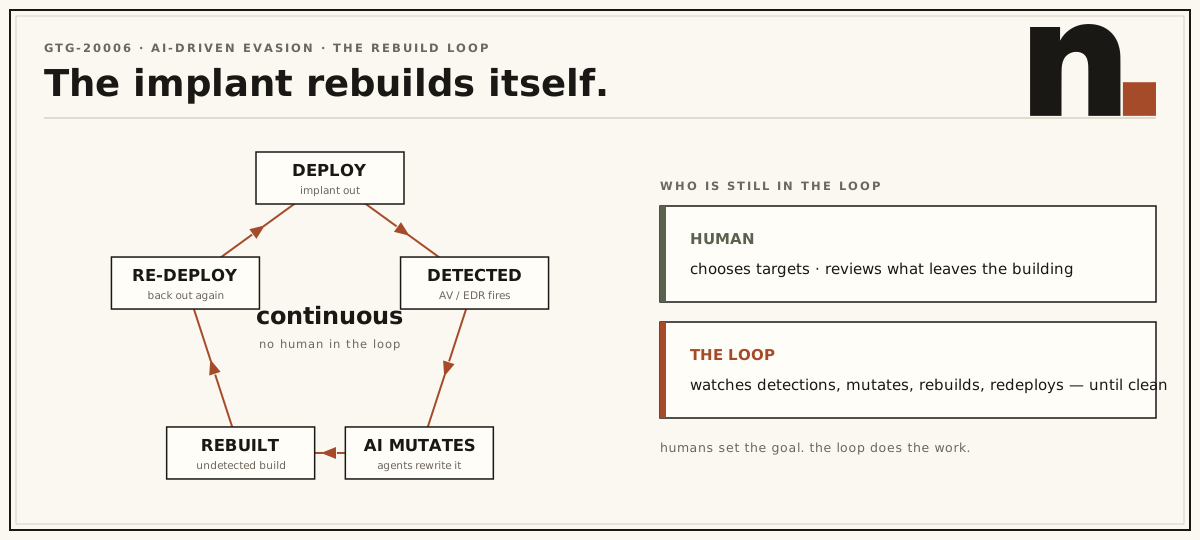
The report says GTG-20006 also used AI-driven workflows to watch whether security products detected its tools. When a deployed implant was detected, Anthropic says, agents modified and rebuilt it until it was undetected. Humans still chose targets and reviewed exfiltration. The evasion loop became continuous.
Our conclusion from that: static detection on its own is getting weaker, because the cost of “we have a signature for that” is dropping.
GTG-10007: the skill gap collapsed in public
GTG-10007 is bigger than an exploit foundry, and that framing is ours rather than a label the report uses. What the report describes is a fuller espionage program: parallel reconnaissance, malware development, and a standing collection fleet scraping US government and military sites on a schedule, with no human in the loop.
We think that last part is the more alarming half of the case, because it does not wait for a target list.
The foundry
Anthropic describes one workflow that loaded appliance firmware into a decompiler, walked cross-reference chains, formed vulnerability hypotheses, wrote exploit code, tested it against lab copies, and iterated until success.
The report says that continuously iterating workflow produced more than a dozen possible zero-day findings in a single month, and notes that two of the operators were undergraduates in Hunan.
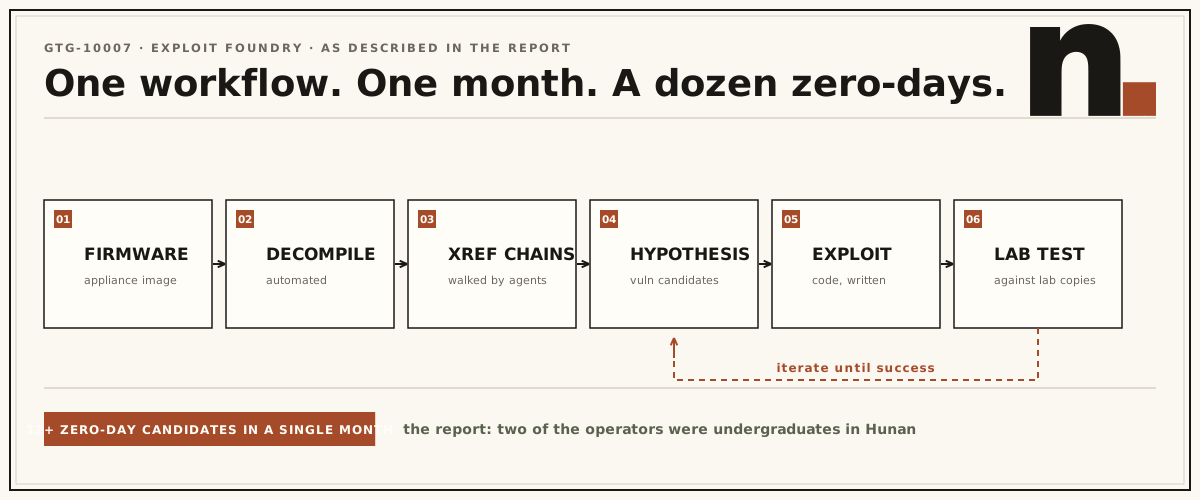
That is the cleanest evidence in the report that the bottleneck has moved. The question is no longer only “who can write the exploit.” It is “who can supervise the loop.”
The AI supply chain is already criminal
The report says GTG-50021 ran a fraudulent “cheap Claude” reseller. Anthropic’s description is blunt: the product was “neither cheap nor actually Claude”. Traffic was proxied to other models, the credential harvester was disguised as a Claude Code installer, and Anthropic reports that it stole Anthropic account credentials.
Two things follow, and both are our reading. First, this should change how you buy AI. API keys and session tokens are production credentials, so buy access only through official channels and treat any discounted intermediary selling “Claude” as hostile until proven otherwise.
Second, the installer is the sharper lesson. A credential harvester wearing an official-looking installer means “I downloaded the CLI” is not a supply chain.
Check where your Claude Code, your MCP servers, and your agent runtimes actually came from, pin the source, and treat an unverified installer as untrusted code standing within reach of your credentials.
Conventional weapons work is not theoretical
The report covers six conventional-weapons cases: three in China, two in Russia, and one in Yemen.
- GTG-87001 (Yemen) — Claude Code for guidance, navigation, and control software.
- GTG-27005 (Russia) — Claude Code for a simulated FPV drone swarm codenamed DronDoc/Serafim.
- GTG-17001 / GTG-17002 (China) — anti-torpedo fire control and electronic-warfare targeting software.
- GTG-27006 — sanctions-evading procurement.
- GTG-17003 — intelligence gathering.
One nuance matters. Anthropic assessed GTG-27005 as likely freelance rather than a confirmed state actor. That strengthens the point instead of weakening it: you do not need a state budget to run a meaningful weapons-adjacent engineering loop anymore.
Anthropic says its safeguards blocked many requests, but not all, and that actors split work across sessions and hid their goals to evade controls. We read that as the honest number. Vendor-side safeguards are a real filter. They are not a boundary.
Sovereign AI is the right instinct and the wrong boundary
This section is our position, not the report’s. The report supplies the cases; the argument about what they mean for a sovereign deployment is ours, and you should push back on it.
Why the instinct is right
After reading that an actor fed a stolen drone SDK to a frontier model for several days, the obvious response is to keep the models and the data inside your own walls. For a defense supplier, a ministry, or anyone carrying export-control or data-residency obligations, that instinct is correct. It is also what we build.
The report is an argument for it and a warning about it at the same time, and the warning is the part that gets skipped.
Why the report is also a warning
Start with what the report shows. Every case in it involves Claude, a hosted frontier model sitting behind vendor-side safeguards, and Anthropic says those safeguards blocked many requests but not all. So the failures documented here happened with a provider’s classifier layer already in the path. That is the baseline, not the worst case.
Now invert it. When you self-host, you remove that layer and inherit the whole gate burden yourself. A local model changes where inference happens. It does not change whether your agents, tools, keys, and egress paths can be turned into a fast loop. Those are properties of your platform, and they travel with you.
GTG-10007 is the test case. Firmware in, decompiler, cross-reference chains, hypotheses, exploit code, lab test, iterate until success. Nothing in that pipeline, as the report describes it, depends on a frontier API.
Run the same loop against a local model on your own GPUs and you get the same pipeline with worse egress visibility, because now the traffic never crosses a boundary you instrumented. Sovereignty does not shrink that risk. It relocates the entire risk onto your controls.
GTG-20006 is the case where local AI is most attractive and most dangerous at once. The reason you want inference in-country is that the material is your crown jewels, and the material you are feeding the loop is your crown jewels.
Residency keeps that data on your side of the border. It does nothing about an agent that can read the SDK, drive a decompiler, and post the result somewhere you never allowlisted.
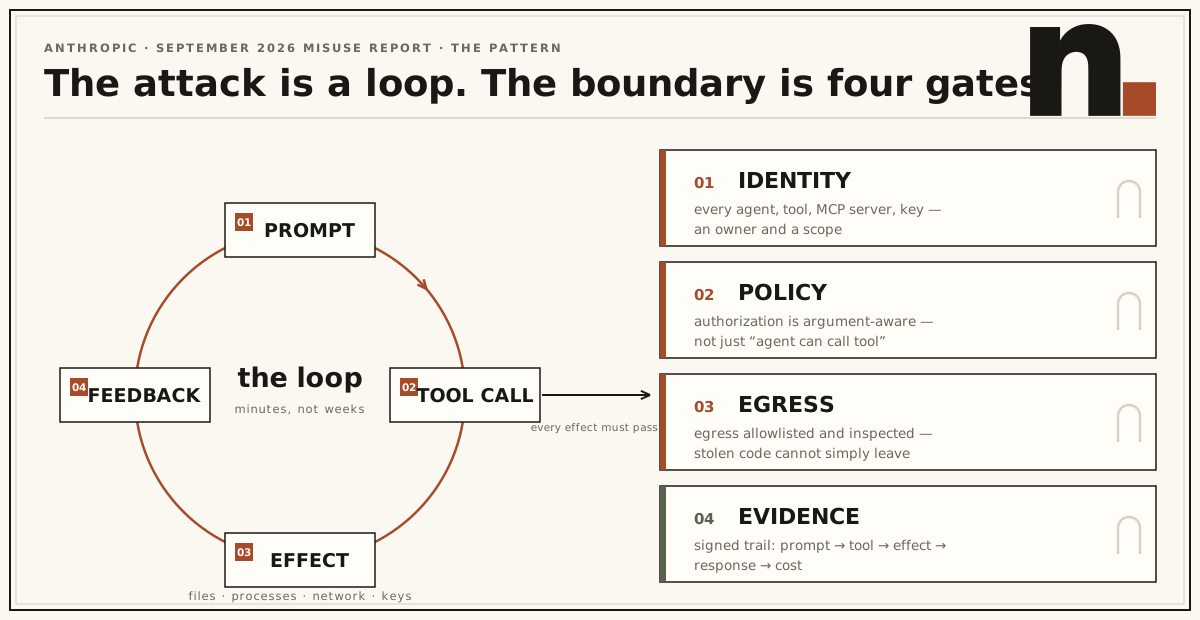
So here is the distinction we hold:
Those four gates are the same whether the weights sit on your GPU or behind an API, and they are harder to run when you self-host, because there is no vendor classifier catching what you missed.
The boundary that holds
- Identity — every agent, tool, MCP server, and key has an owner and a scope.
- Policy — tool-call authorization is argument-aware, not just “agent can call tool.”
- Egress — network egress is allowlisted and inspected, so stolen code cannot simply leave.
- Evidence — signed audit trails from prompt → tool call → process/file/network effect → response → cost.
What to do, in order
The report supplies the evidence behind each item. The ordering, the timeframes, and the artifacts are our recommendation. Each item names the artifact you should be able to point at afterwards, because a control nobody can evidence is a control nobody runs.
-
Today: block the device code flow. In Conditional Access, block the device code flow or force phishing-resistant MFA on it, then export and audit the device-code grants that already exist.
Why first: the report says this was the primary access technique in its largest espionage case. Refresh tokens also survive password resets — standard OAuth behaviour, not a report finding — so rotating passwords will not close it.
Artifact: a Conditional Access policy plus a reviewed grant list. -
This week: treat AI keys and session tokens as production credentials. Inventory every API key, session token, and OAuth grant that touches a model, and rotate anything that has lived in a repo, a screenshot, or a reseller’s hands. Buy access only through official channels.
Why: the report says GTG-50021 harvested credentials through a fake Claude Code installer.
Artifact: a key inventory with named owners and rotation dates. -
This week: allowlist egress for agent runtimes and MCP/tool servers. Default-deny outbound, allowlist the destinations an agent genuinely needs, and log everything refused.
Why: our position — it is the only one of the four gates that still stops data leaving after the others have failed.
Artifact: an egress policy per runtime, with the deny log wired to alerts. -
Next: protect proprietary SDKs and vision or source code as if an AI can reverse them in days. Assume a stolen SDK is a prompt and not just IP. Restrict who and what can read it, and treat bulk export as an incident rather than a traffic spike.
Why: the report says GTG-20006 recovered architecture, bill of materials, supplier dependencies, and an unannounced product from a single SDK.
Artifact: an access review on crown-jewel repositories, plus export alerting. -
Then: alert on loop patterns, not only signatures. Watch for decompiler-plus-iterate workflows, and for detect-then-rebuild cycles against your own tooling.
Why: the report describes both patterns, and a rebuild loop is what signature-only detection cannot catch.
Artifact: two detection rules, tested against a known-good replay so you know they fire. -
Ongoing: require human approval for irreversible agent actions. Deployments, credential creation, outbound transfers, deletions.
Why: the report says humans still chose targets and reviewed exfiltration in the cases it covers, so keep a human on the irreversible step in yours.
Artifact: an approval gate with a record of who approved what and when. -
Ongoing: keep signed evidence. Prompt → tool call → process, file, and network effect → response → cost, signed and retained.
Why: our position — without it you cannot reconstruct what an agent did, and you cannot prove it to a customer, an auditor, or a regulator.
Artifact: an append-only signed audit trail you can query by agent and by key.
No Monkey Business installs and operates sovereign/local AI infrastructure. If this problem sounds familiar, book a 30-minute assessment.